The firm
Six security analysts deliver VAPT engagements, IT audits and ISO 27001 implementations.
What made the work hard
- Testing sometimes started before written authorisation arrived.
- Re-tests weren't scoped and dragged on.
- Access details were shared over email.
How they set up MSMEPulse
- Chose Cybersecurity & IT Audit at signup, with security assessment (VAPT), ISO 27001 and managed IT templates.
- Made written authorisation a compulsory checklist item before testing.
- Included one re-test in every proposal, with a fix window.
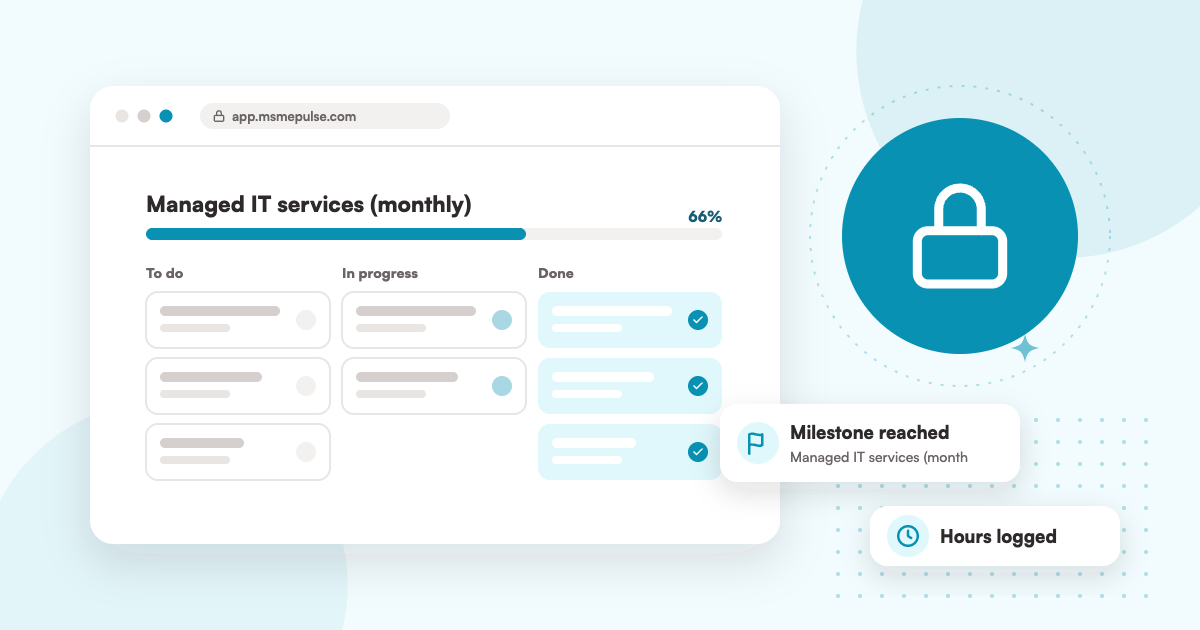
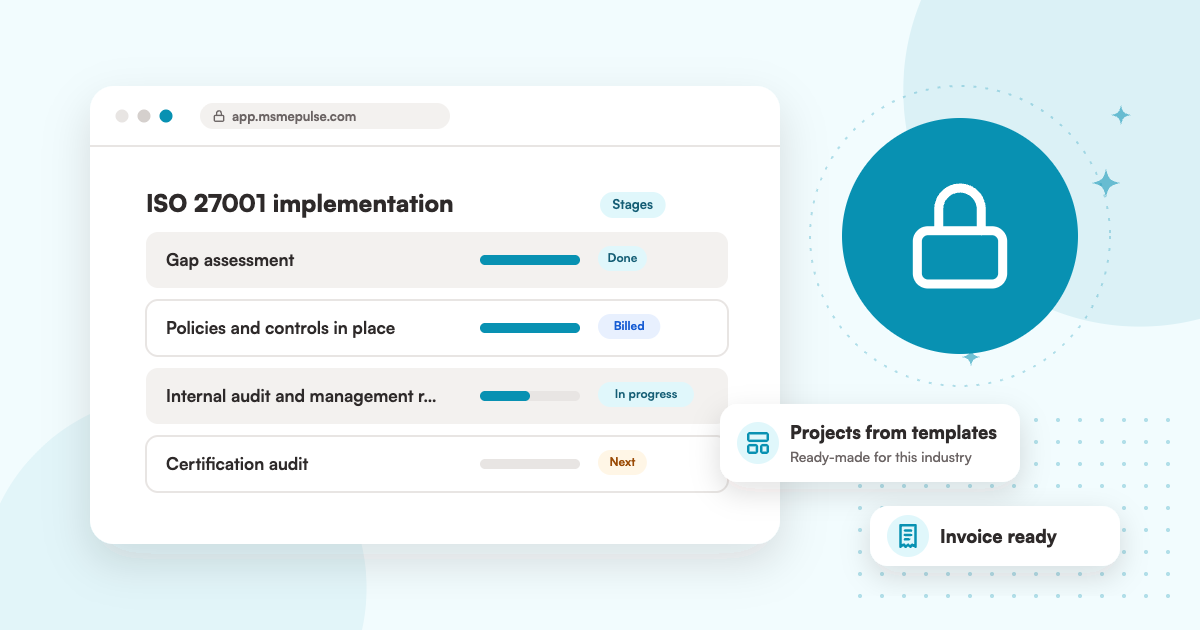
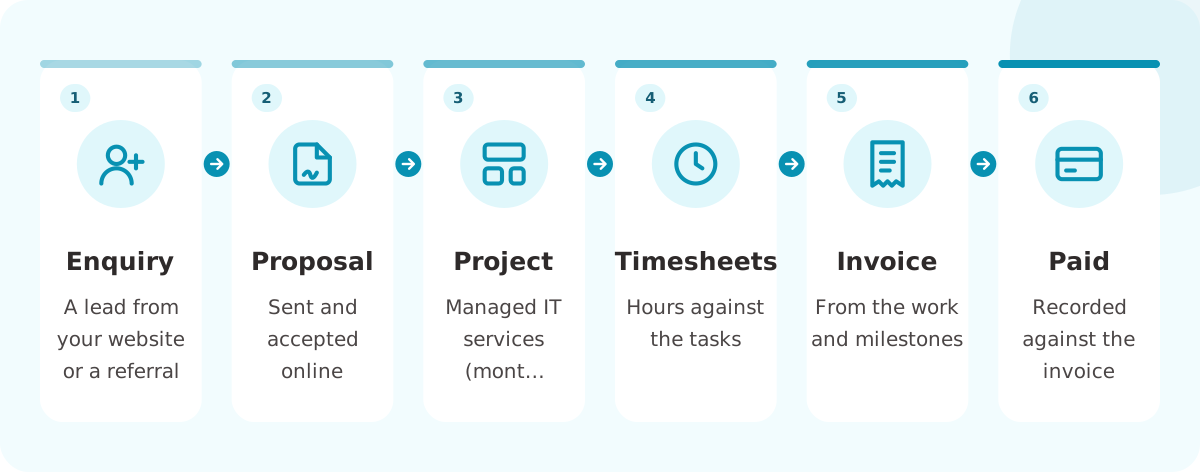
The templates for Cybersecurity & IT Audit in MSMEPulse: Managed IT services (monthly), Security assessment (VAPT), ISO 27001 implementation.
A typical month
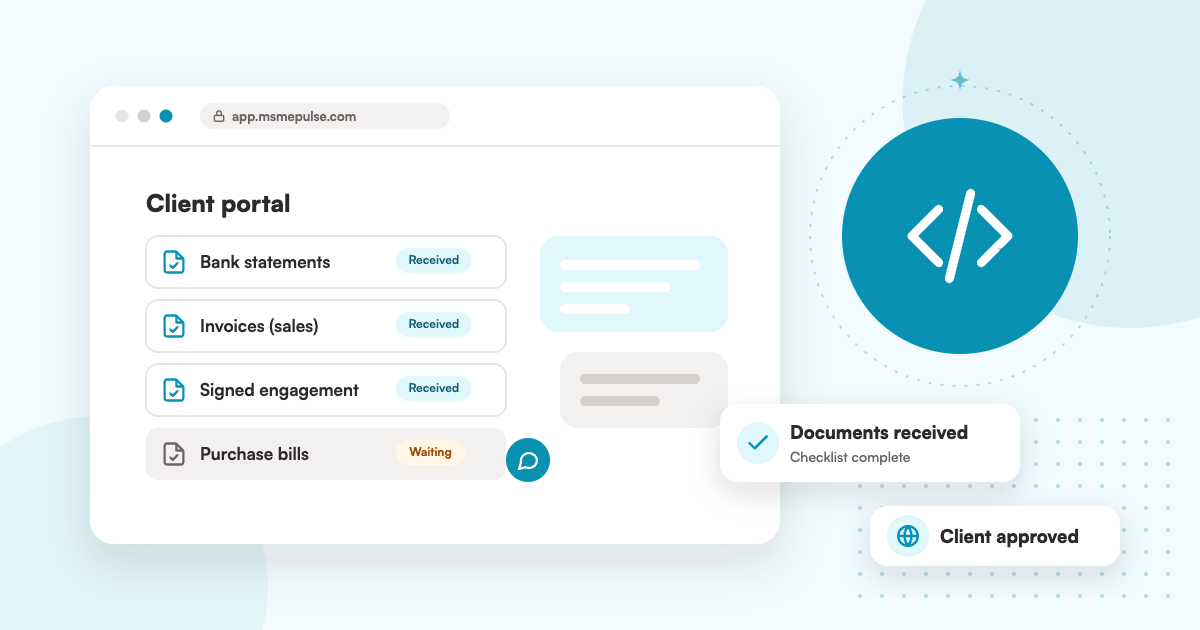
Each assessment starts with scope and authorisation on the checklist; testing can't start until they're in. Critical findings are reported straight away. After the report, the client has an agreed window to fix, then the re-test and closure report. Access details come through the portal, not email.
What changes
- No testing without authorisation on record.
- Re-tests are scoped and time-boxed.
- Sensitive access details stay out of email.
See it with your own industry
Sign up, choose your industry, and install sample data from Settings. You'll get a realistic business like this one, with projects from your industry's templates, clients, timesheets and invoices, to explore before adding your own records.